
Guardian Announces Vanguard
A security audit designed to protect onchain teams facing unprecedented cyber risk.
Along with Vanguard, we are announcing $1,000,000 in security audit funding.
Onchain finance is under attack.
Frontier AI allows anyone to carry out sophisticated attacks against even the slightest gap in an organization’s defenses.
Tokenized assets and DeFi protocols are among the first to be targeted with this new technology, with billions at risk.
Enter: Vanguard
Vanguard is a security audit designed to provide teams the 100% surface area coverage they need to ship high risk releases confidently in the agentic cyber era.
Vanguard combines every valuable method across every uncovered attack surface, leaving no gaps for threat actors.
This is the 360° coverage required to secure digital assets in today’s threat landscape.
Two Teams, One Codebase
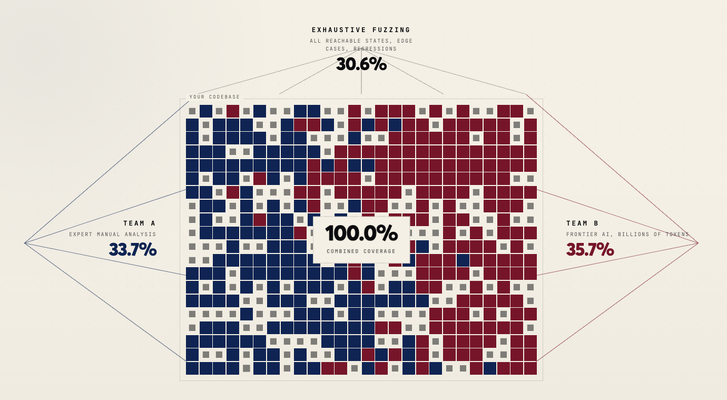
The Vanguard model starts with two teams both securing the same codebase.
Team A & B use different approaches, both of which uncover unique findings that the other would miss.
Team A uses tried and true auditing methods: expert manual review and deep invariant fuzzing to cover every possible application state.
Team B drives billions of AI tokens into every corner of the codebase, saturating everything frontier models are capable of finding.
Helix, the AI Auditor
Helix is the leading AI Auditor powering Team B with the world’s deepest agentic security audit.
Helix covers every single call flow and execution path without fail while scaling compute to billions of tokens and unifying context across an entire review.
Already Helix has proven itself with confirmed bug bounties in many of the most respected protocols in DeFi, with many more on the way.
Helix marks the beginning of the AI + Human era in onchain security.
AI performs an exhaustive search for every possible bug and exploit, humans verify the context, configuration, and depth. Only human verified findings enter the final result.
A $100,000 Defender Contest
After the two teams conduct a full audit on the codebase, Guardian sponsors a $100,000 Defender contest on the same scope as a cross-check.
The public Defender contest opens the audited scope to a global network of independent human researchers and AI Auditors.
Defender serves as a final barrier giving absolute assurance from the broader security community and the entire landscape of AI auditors.
Then an Evergreen Bug Bounty
After the Defender contest Guardian then hosts an evergreen bug bounty for the scope with up to $50,000 in Critical matching.
The Weakest Link Moved Offchain
With battle-hardened smart contracts, the onchain portion of financial applications today is no longer the weakest link.
The largest exploits of 2026 all came from offchain gaps:
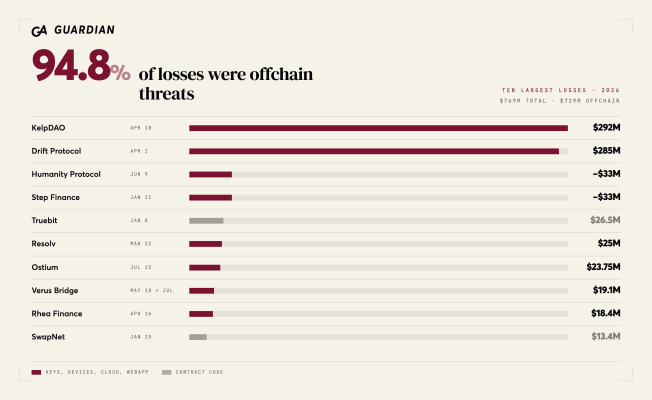
This trend is only accelerating with the progression of AI Agents.
Since 2025, Guardian has been building a fierce offchain security department to combat the growing Web2 risk surface:
- Webapps
- Keepers
- Cloud infrastructure
- Network perimeters
- OpSec
Carlos Polop heads the offchain department
Heading the offchain department at Guardian is the distinguished cybersecurity researcher Carlos Polop.
Carlos is most widely known for creating the biggest free cybersecurity wiki at @hacktricks_live as well as the widely used privilege escalation tool PEASS.
In 2025, Carlos coached team Europe to victory in the International Cybersecurity Challenge in Japan.
Carlos brings extensive experience across every vertical that threatens Web3 applications today, and has built the offchain department at Guardian around that foundation.
To date, Guardian’s offchain services have secured critical threat surfaces for some of the largest teams in DeFi. Trusted by LayerZero, GMX, USDT0 and Avantis among many others.
Every Vanguard audit comes with half of the package cost back as credits towards offchain services, to cover the critical surfaces that are most likely to lead to compromise and exploit in 2026.
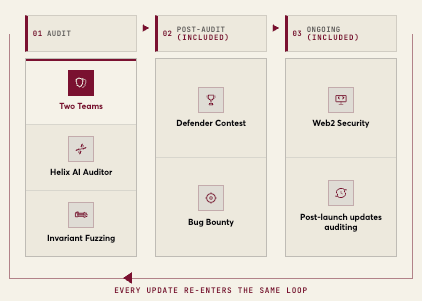
Six Months of Post-Launch Review
A holistic security solution would not be complete without continuous review of updates post-launch.
Teams often make adjustments and add incremental features after launch, oftentimes without the same security oversight.
For many, these small updates are a large risk.
For this reason, a Guardian Vanguard audit includes continuous review of updates made to the scope post-audit for a 6-month period after launch.
Every update meets the same security standard and gets reviewed by the same eyes and systems that signed off on the original version.
Vanguard Is Available Today
Guardian Vanguard is our response to the imminent AI cyber threat and the growing Web2 risk surface in onchain finance.
Starting today Vanguard is available to protocol teams in need of complete security coverage: guardian.security/vanguard
$1,000,000 in Security Audit Grants
With the release of Vanguard, Guardian is putting up $1,000,000 in security grant funding for teams shipping consequential products in DeFi and tokenization.
Teams selected based on track record and ecosystem impact can receive up to a full audit grant from Guardian.
Teams interested in participating in the $1,000,000 security audit grants program can apply here.
Ready to cover every surface with Vanguard?
Guardian provides institutional-grade web3 security to the best teams in the industry.