
Guardian Announces Managed Security
A security backbone for onchain organizations, run by Guardian engineers around the clock.
In response to heightened risk across the blockchain ecosystem, Managed Security is available today for digital asset teams.
Onchain finance is entering a storm.
Frontier AI is changing the economics of cyberattacks. Agents now find and exploit vulnerabilities in minutes.
Digital asset teams are target number one: the money is right there, it moves instantly, and recourse is minimal.
Point-in-time audits alone can no longer keep up.
The new assumption is that there will be vulnerabilities. What matters is the systems and people in place to detect and resolve them in real time.
Enter: Managed Security
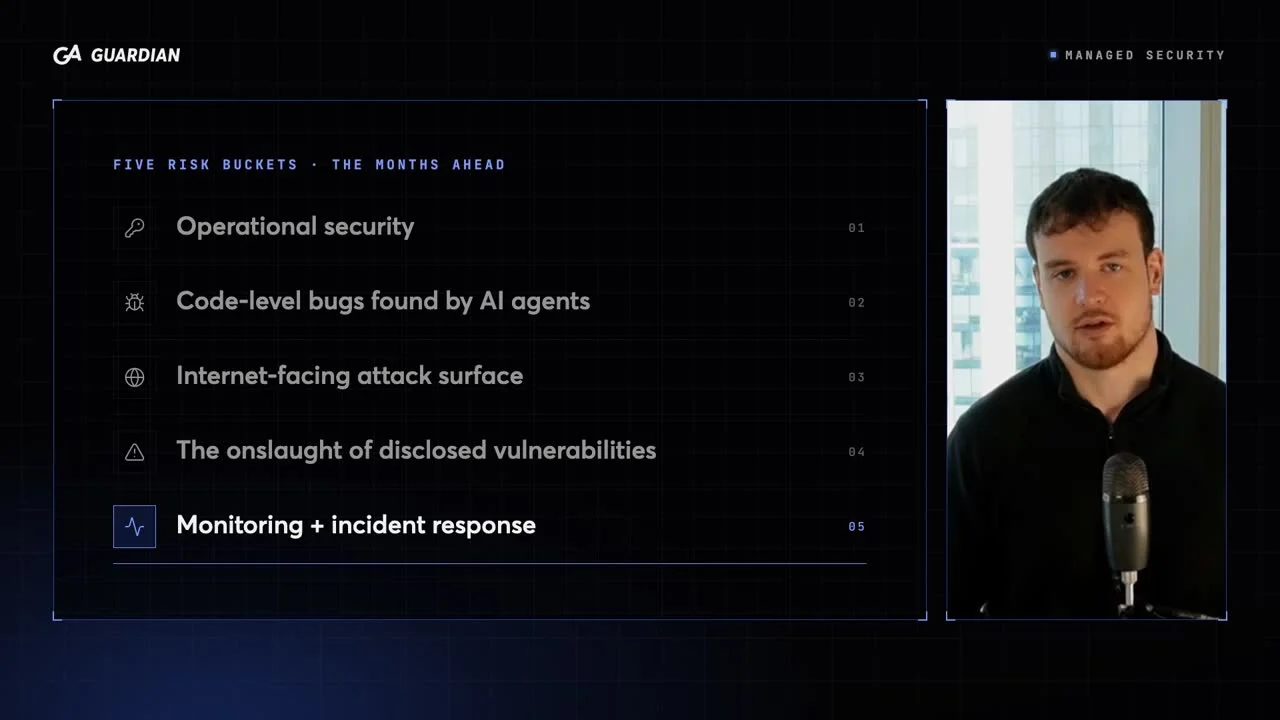
Managed Security covers the five areas of risk every digital asset team needs a plan for:
- Operational security
- Code-level vulnerabilities
- Internet-facing attack surface
- Security advisories
- Monitoring and incident response
Operational Security
It starts with operational security.
We map every contract, role, signer, dependency, and piece of infrastructure into a live threat model of every path to your funds.
Every change to that map is watched. When a notable threat emerges, a Guardian engineer is on it.
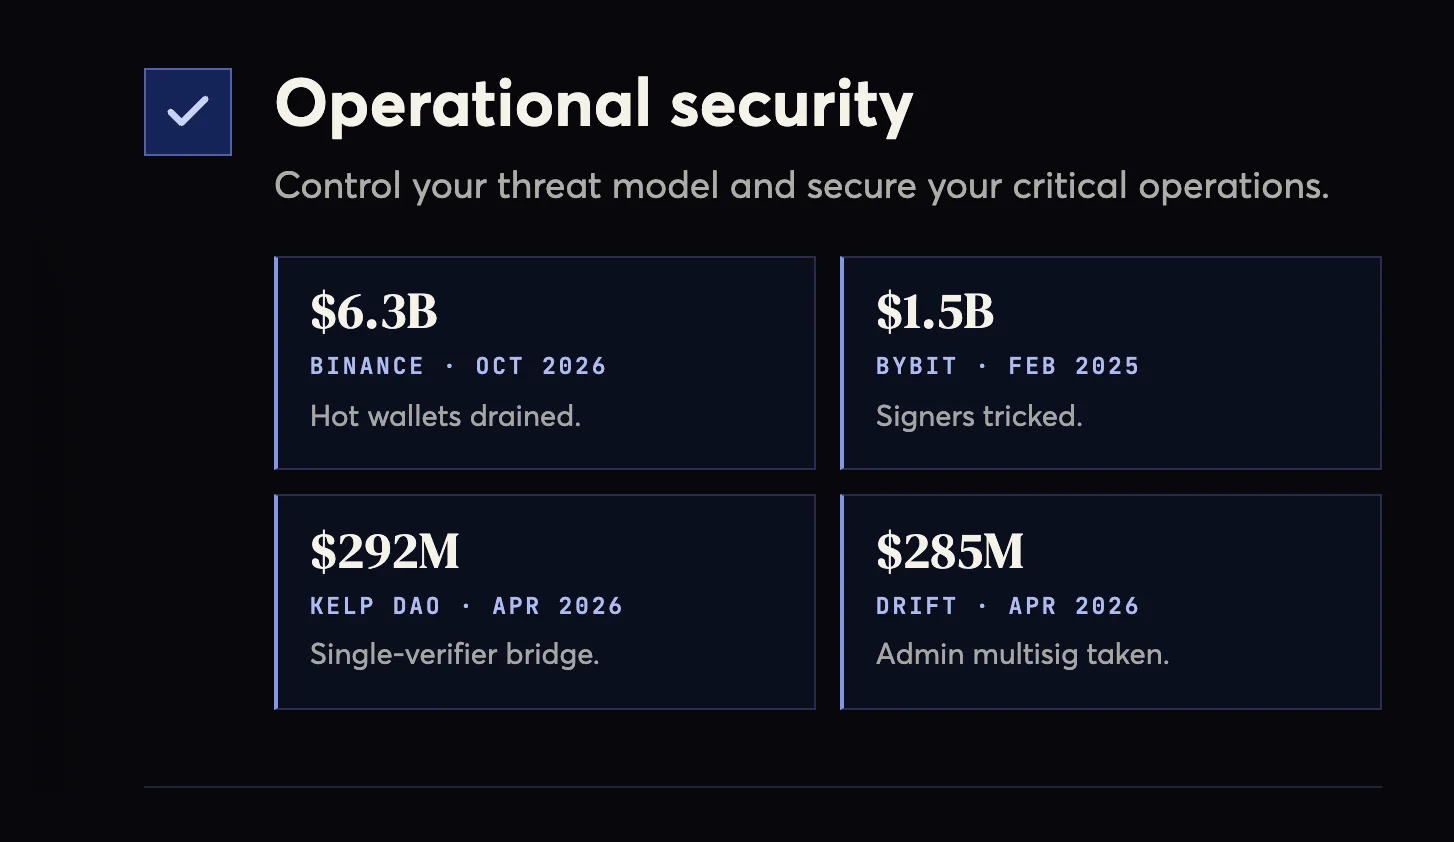
Most teams carry far more day-to-day risk than they should.
Onboarding removes it with the right trust model, signing setup, and controls.
High-risk operations like multisig deployments and configuration changes get a rapid third-party review from a Guardian engineer.
Continuous Vulnerability Testing
Next, the code.
Helix, Guardian’s AI auditor, maps your entire system: smart contracts, APIs, web apps, keepers, and offchain automation.
Swarms of agents spend billions of tokens to find, validate, and prove vulnerabilities, continuously, as your system changes.
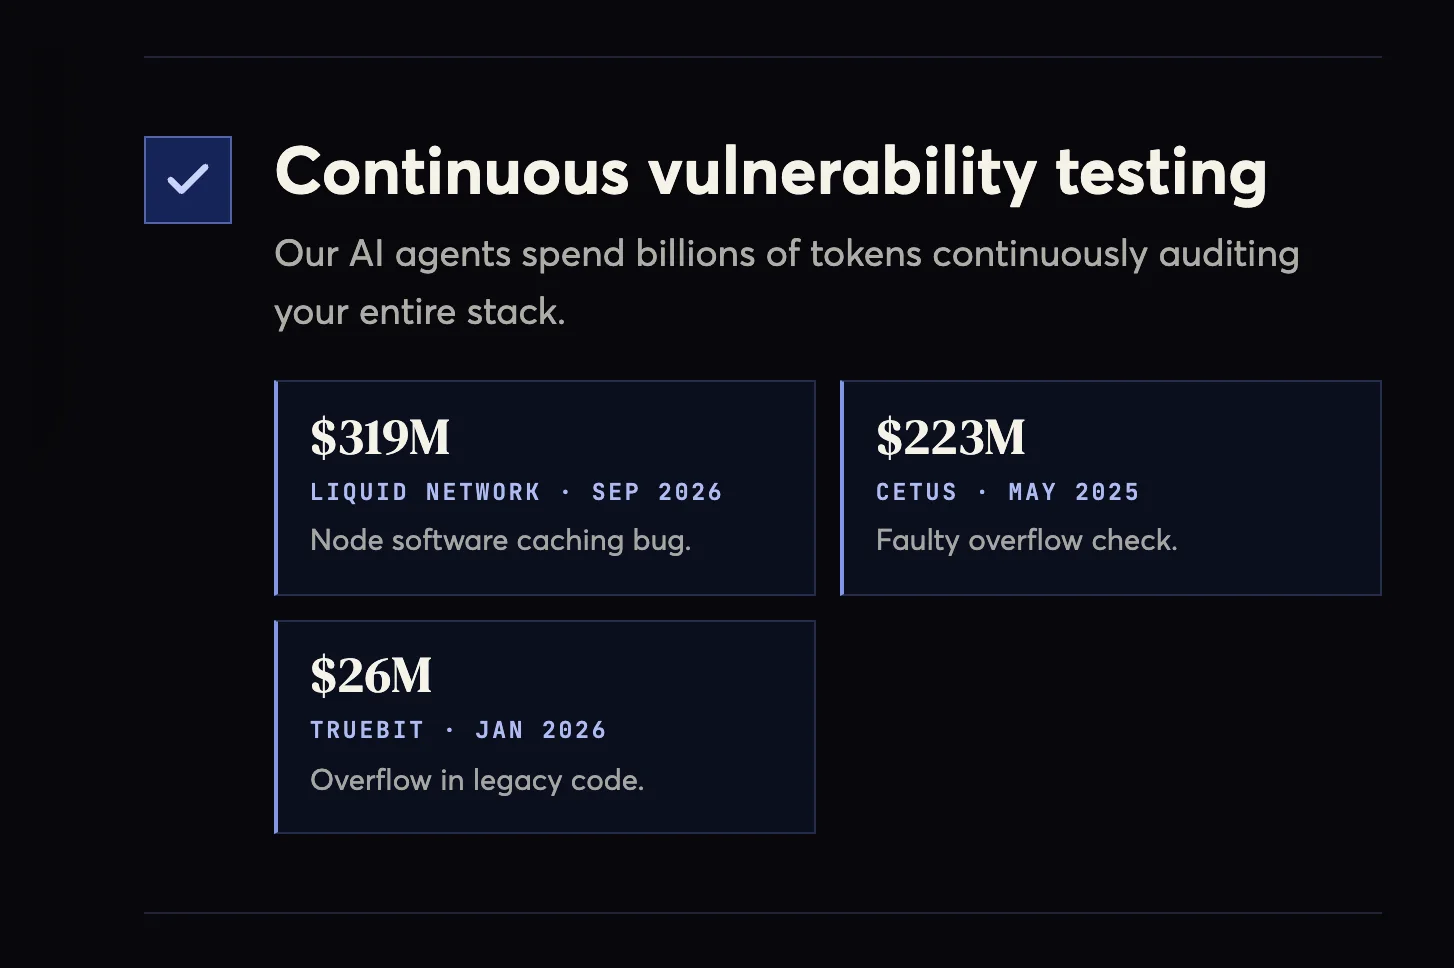
Findings never land on your team as overhead.
Guardian engineers who know your stack work through every finding and prepare the patches with you.
We also run your bug bounty, on our platform or yours, with full triage of every submission.
Defend Your Web Surface
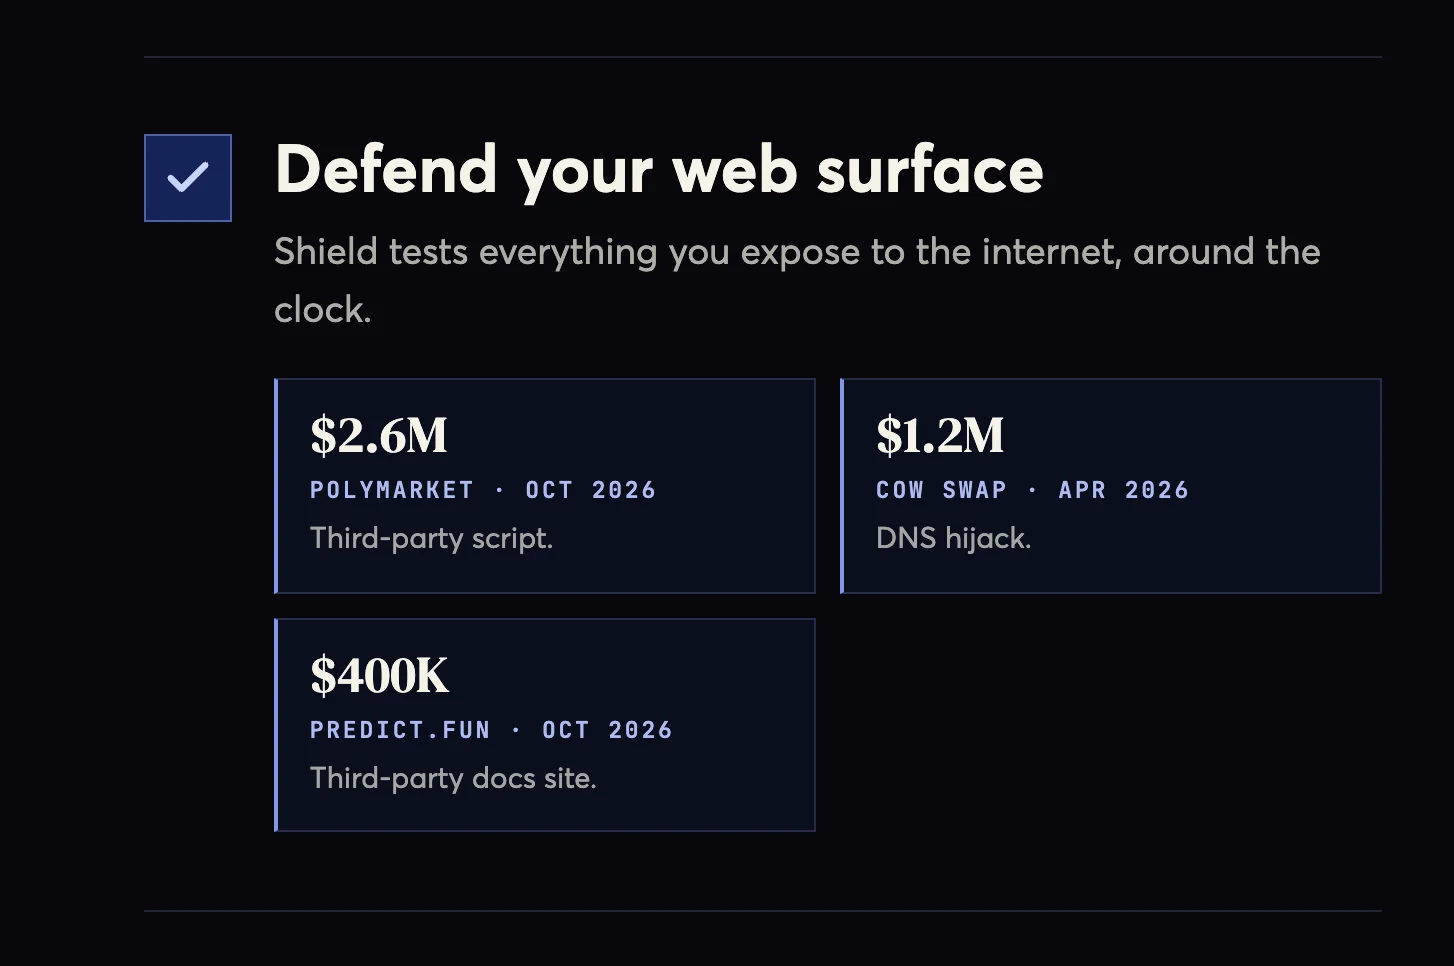
Many of this year’s hacks never touched a smart contract.
Shield, Guardian’s attack surface management system, discovers every domain, website, IP, cloud service, and repository you expose.
Then Shield runs agents and pentests against it around the clock.
The Onslaught of Security Advisories
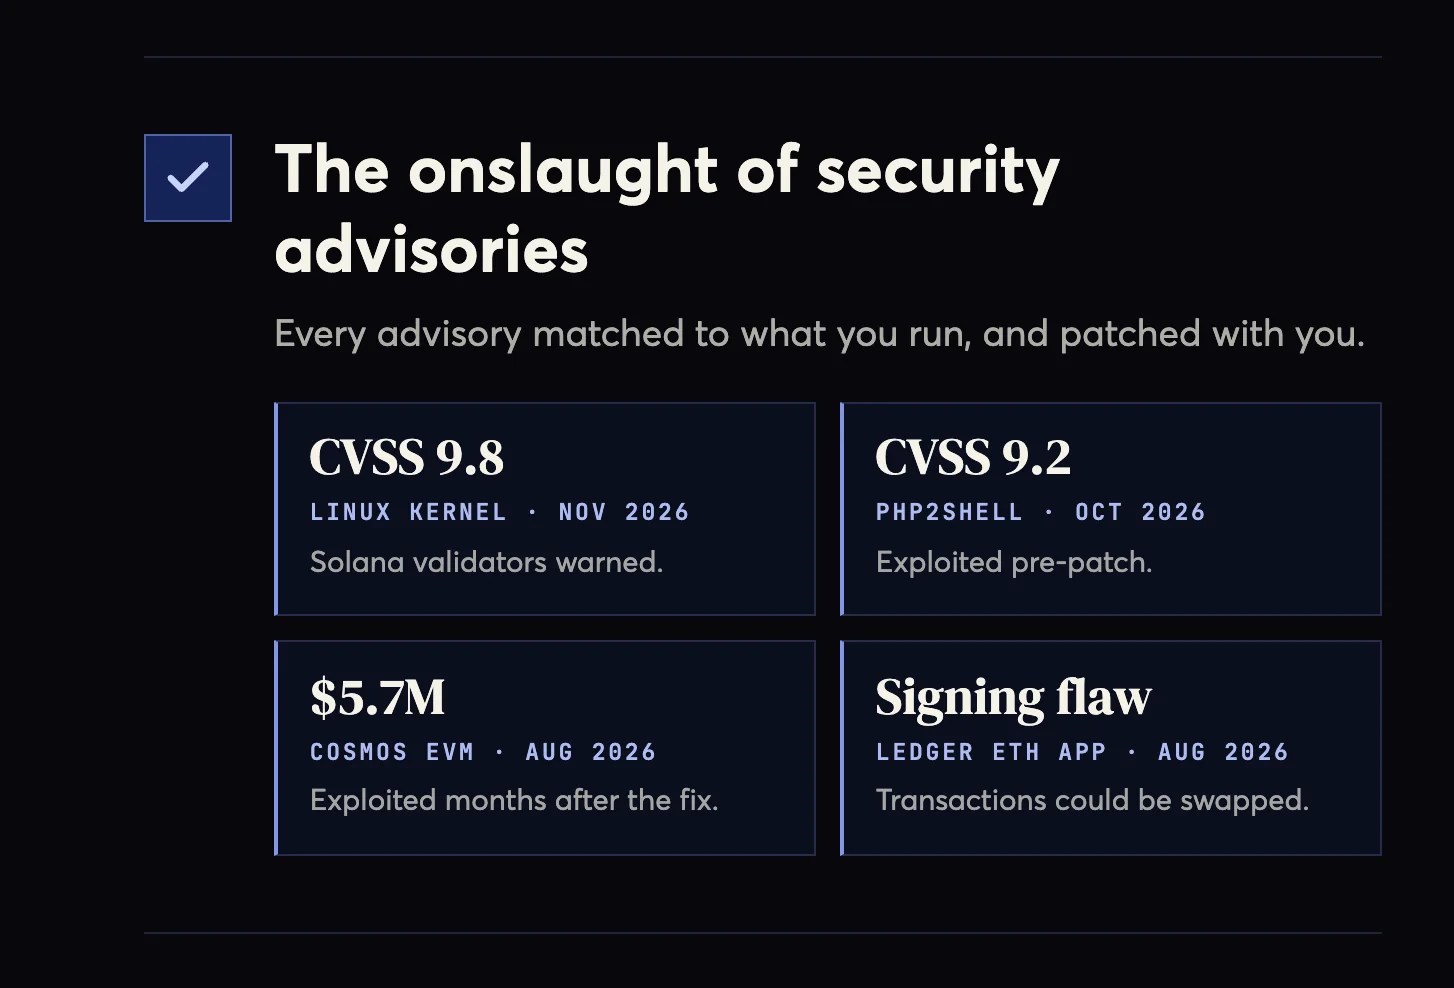
Then there’s everyone else’s code.
Hundreds of disclosures are coming for the frameworks we all rely on.
We ingest advisories from many sources in real time, match them to your stack, assess your exposure, and get the patch through with your team.
24/7 Monitoring and Incident Response
Finally, monitoring and response.
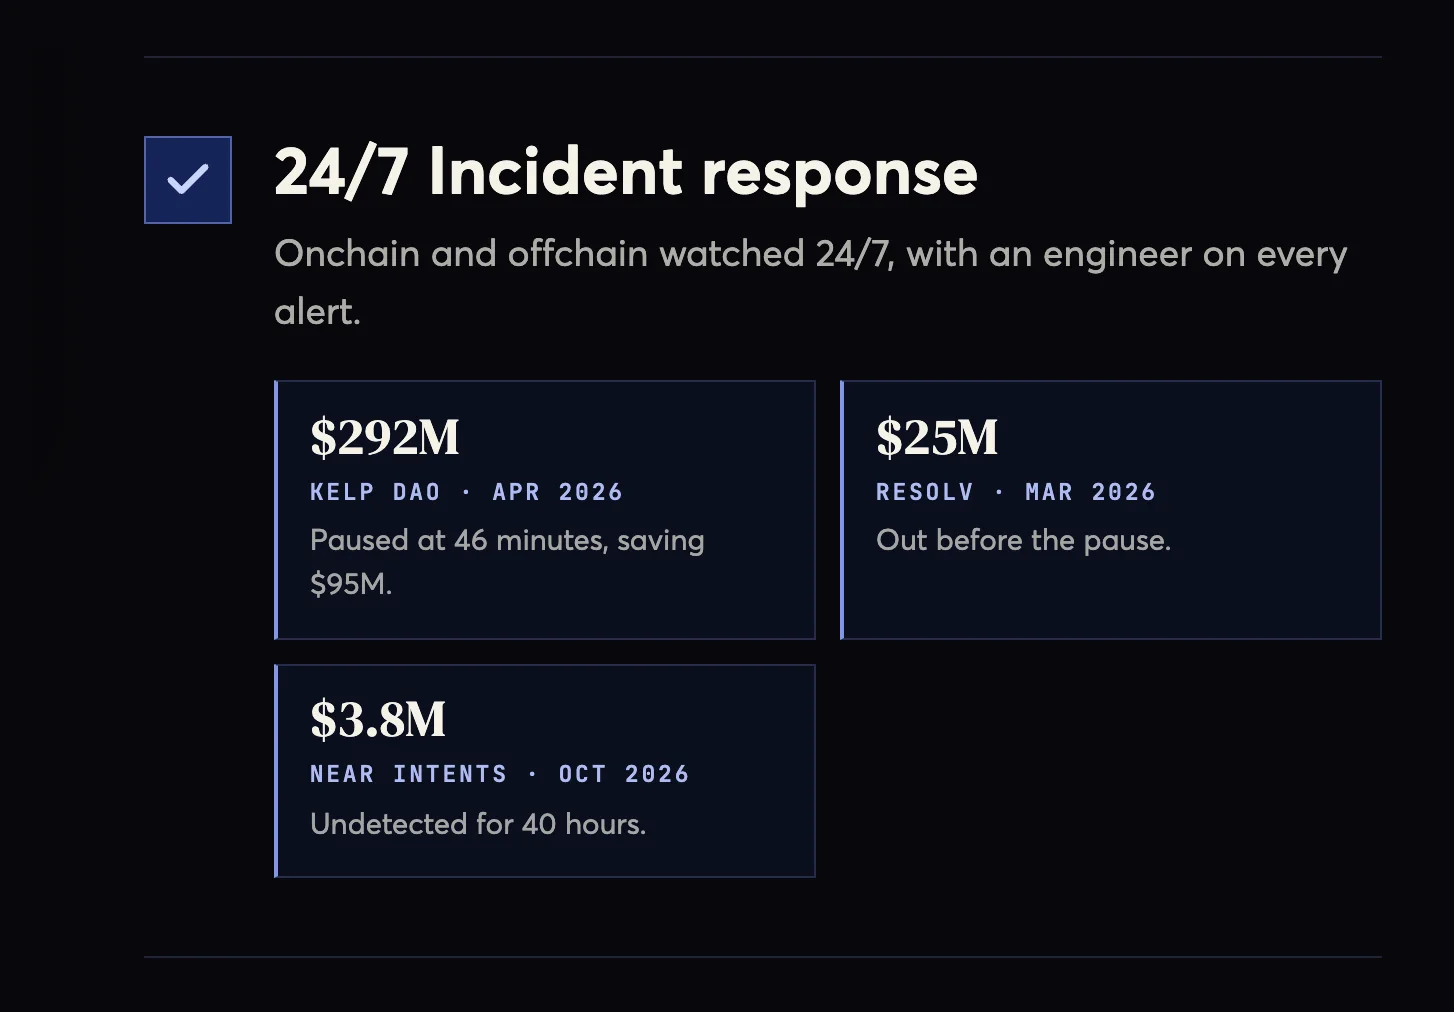
Guardian monitoring ships with out-of-the-box detectors plus custom rules and actions, including automated pauses.
Your existing monitoring streams into our global 24/7 MDR team.
Onchain and offchain, watched around the clock, with a 15-minute SLA on Critical alerts.
A Trust Center for Compliance
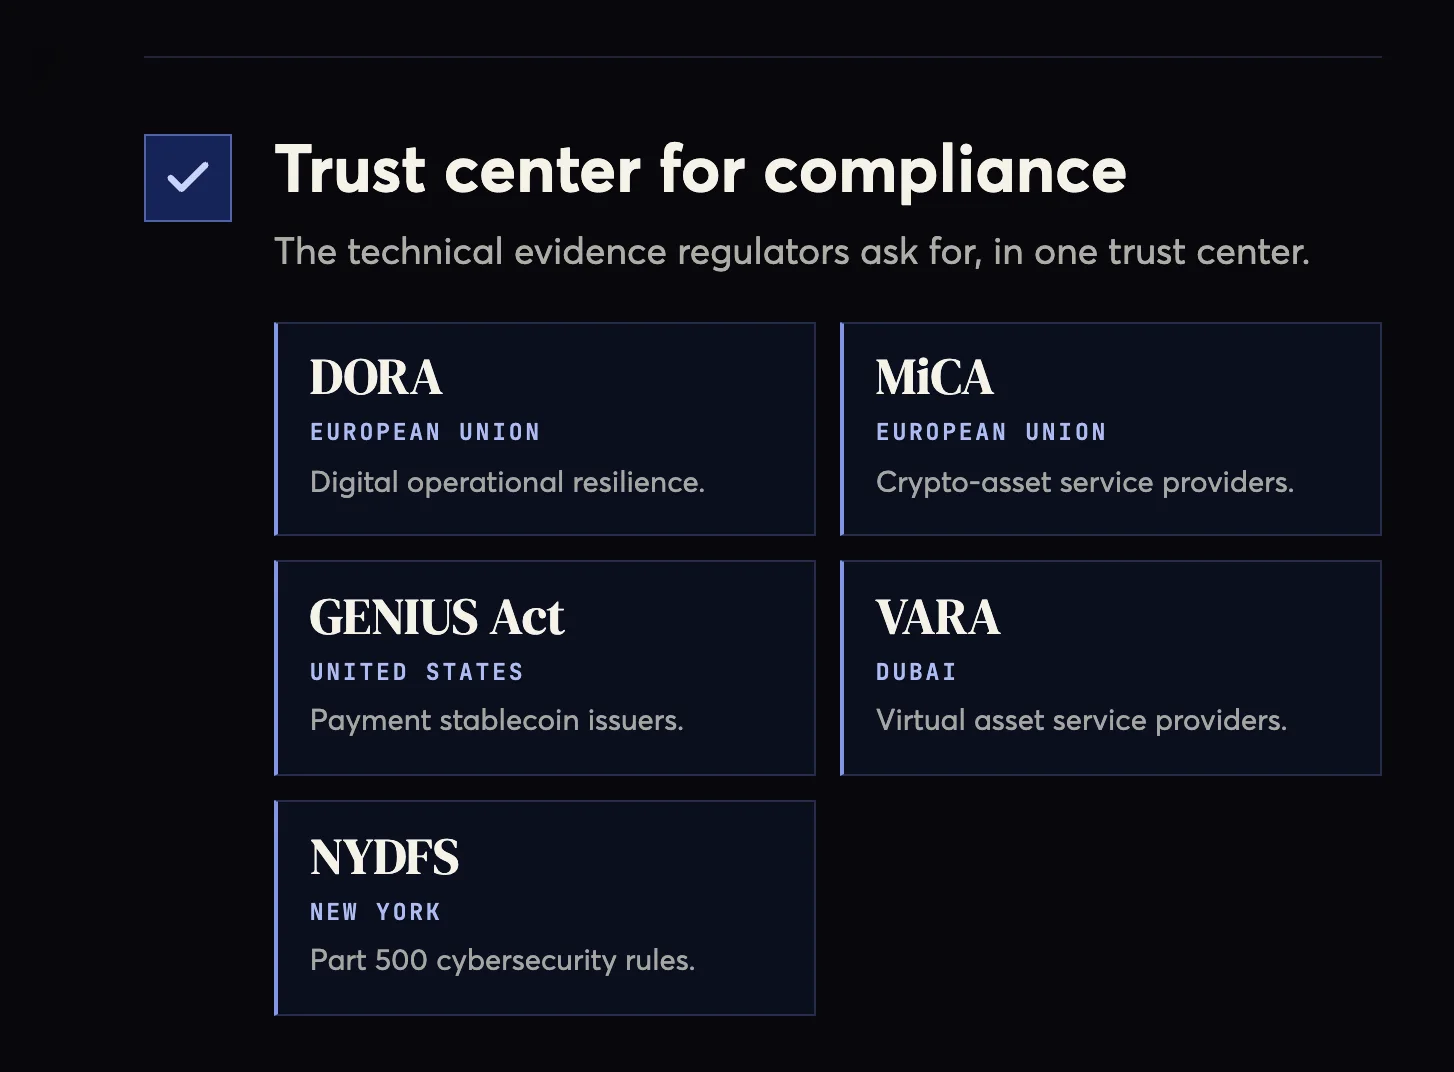
All of it comes with a hosted trust center and the technical evidence regulators ask for under DORA, MiCA, the GENIUS Act, VARA, NYDFS, and more.
Why Not Build It In-House?
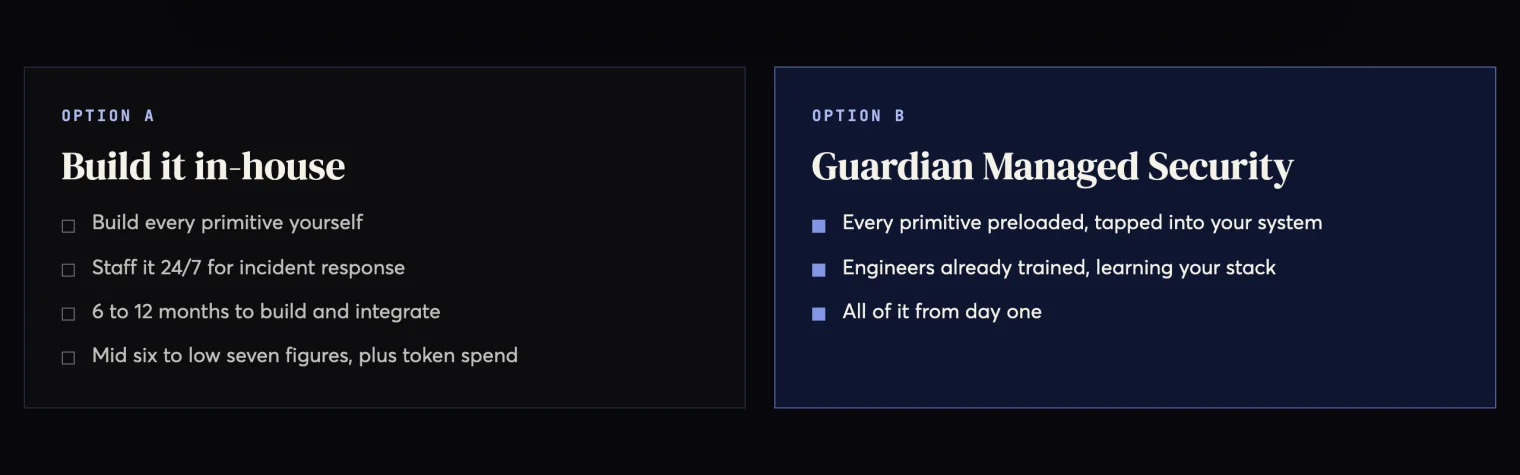
Building these primitives and staffing them 24/7 takes 6 to 12 months and mid six to low seven figures, plus token spend.
Managed Security gives you every primitive, and engineers already trained on it, from day one.
Getting Started
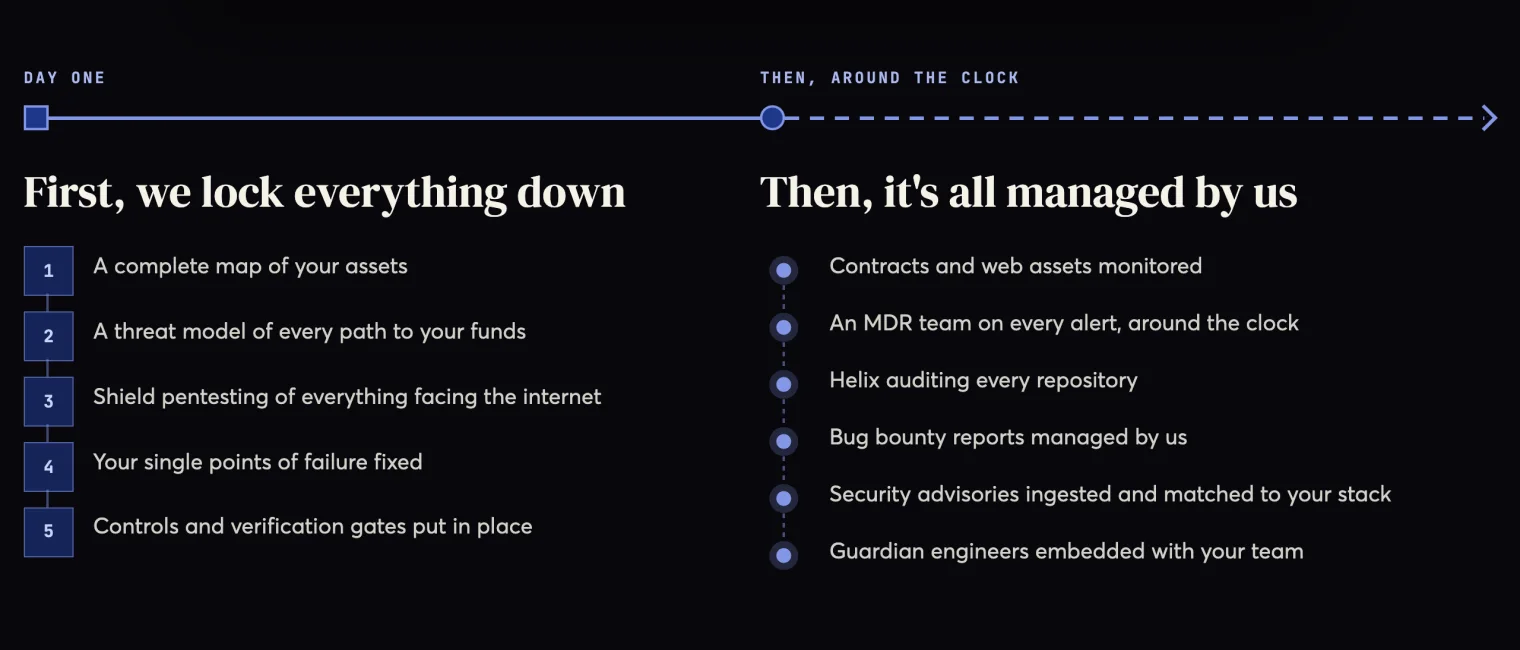
On day one, we lock everything down:
- A complete map of your assets
- A threat model of every path to your funds
- Shield pentesting of everything facing the internet
- Your single points of failure fixed
- Controls and verification gates put in place
Then it’s all managed by us, around the clock.
Least privilege, read-only
Managed Security runs on least privilege and is read-only:
- Monitoring and threat models run on public chain state
- Shield sees only what an attacker sees
- Helix needs read access to the repos you choose
Your team keeps full access to our alerts, monitors, and tools.
Five Years With the Most Targeted Teams
For five years, Guardian has worked with the most targeted teams in DeFi and digital assets.
$45B+ in assets secured for 150+ teams, including USDT0, Ethena, GMX, and LayerZero.
The 90-Day Guarantee
We are confident enough to guarantee this is a necessary piece of protocol operations.
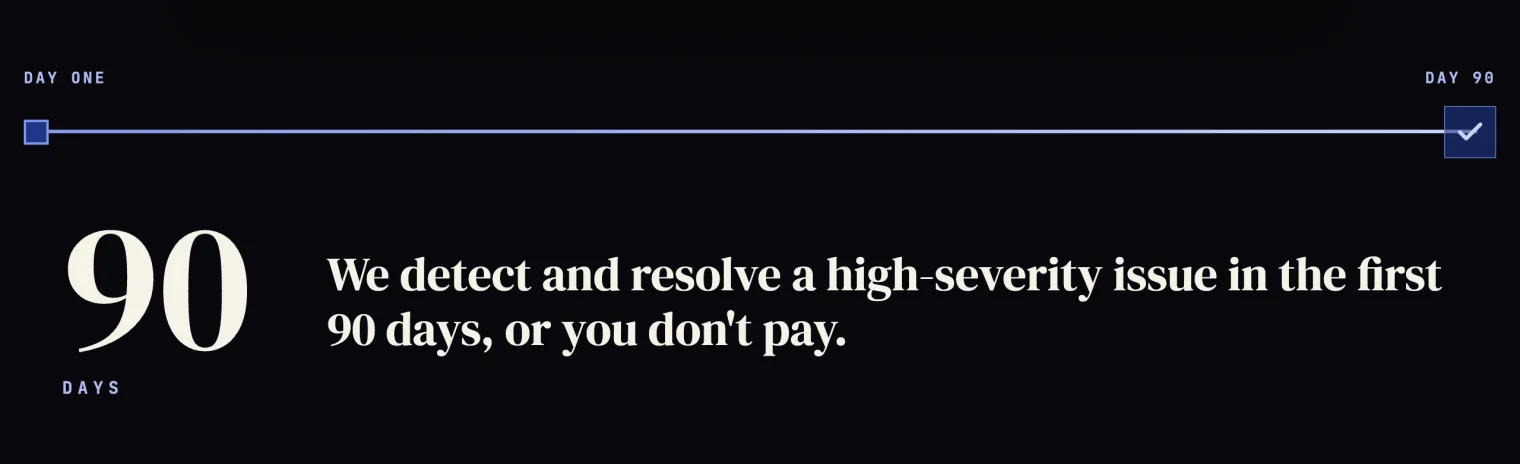
Within the first 90 days, we detect and resolve a high-severity issue with funds at risk or services that could be disrupted, or you don’t pay.
Managed Security Is Available Today
Guardian Managed Security is our response to the AI cyber storm ahead.
Starting today, it is available to digital asset platforms and DeFi protocols: guardian.security/managed-security
Watch the full walkthrough and book a call here.
Ready to endure the AI cyber storm?
Guardian provides institutional-grade web3 security to the best teams in the industry.